This article documents in detail the complete construction of a blog comment system with multi-layer security, smart content moderation, and multi-layer anti-spam rate limiting, covering the implementation of core technologies including setting up the Gin framework, JWT authentication, multiple rate limits by IP/email/content, human verification, and AI content moderation.
Table of Contents
Project Overview and Architecture Design Tech Stack Selection and Project Structure The Multi-Layer Security System Database Design and Model Relationships Core Comment Feature Implementation Smart Content Moderation System Rate Limiting and Anti-Spam Mechanism Deployment and Operations Practice Summary and Outlook
1. Project Overview and Architecture Design 1.1 Project Background As the blog’s content kept growing, I needed a safe, reliable, and feature-complete comment system to interact with readers. Traditional third-party comment systems (like Disqus and Gitment) have flaws such as uncontrollable data, slow loading, and privacy issues. So I decided to build my own comment system, which needed to meet the following core requirements:
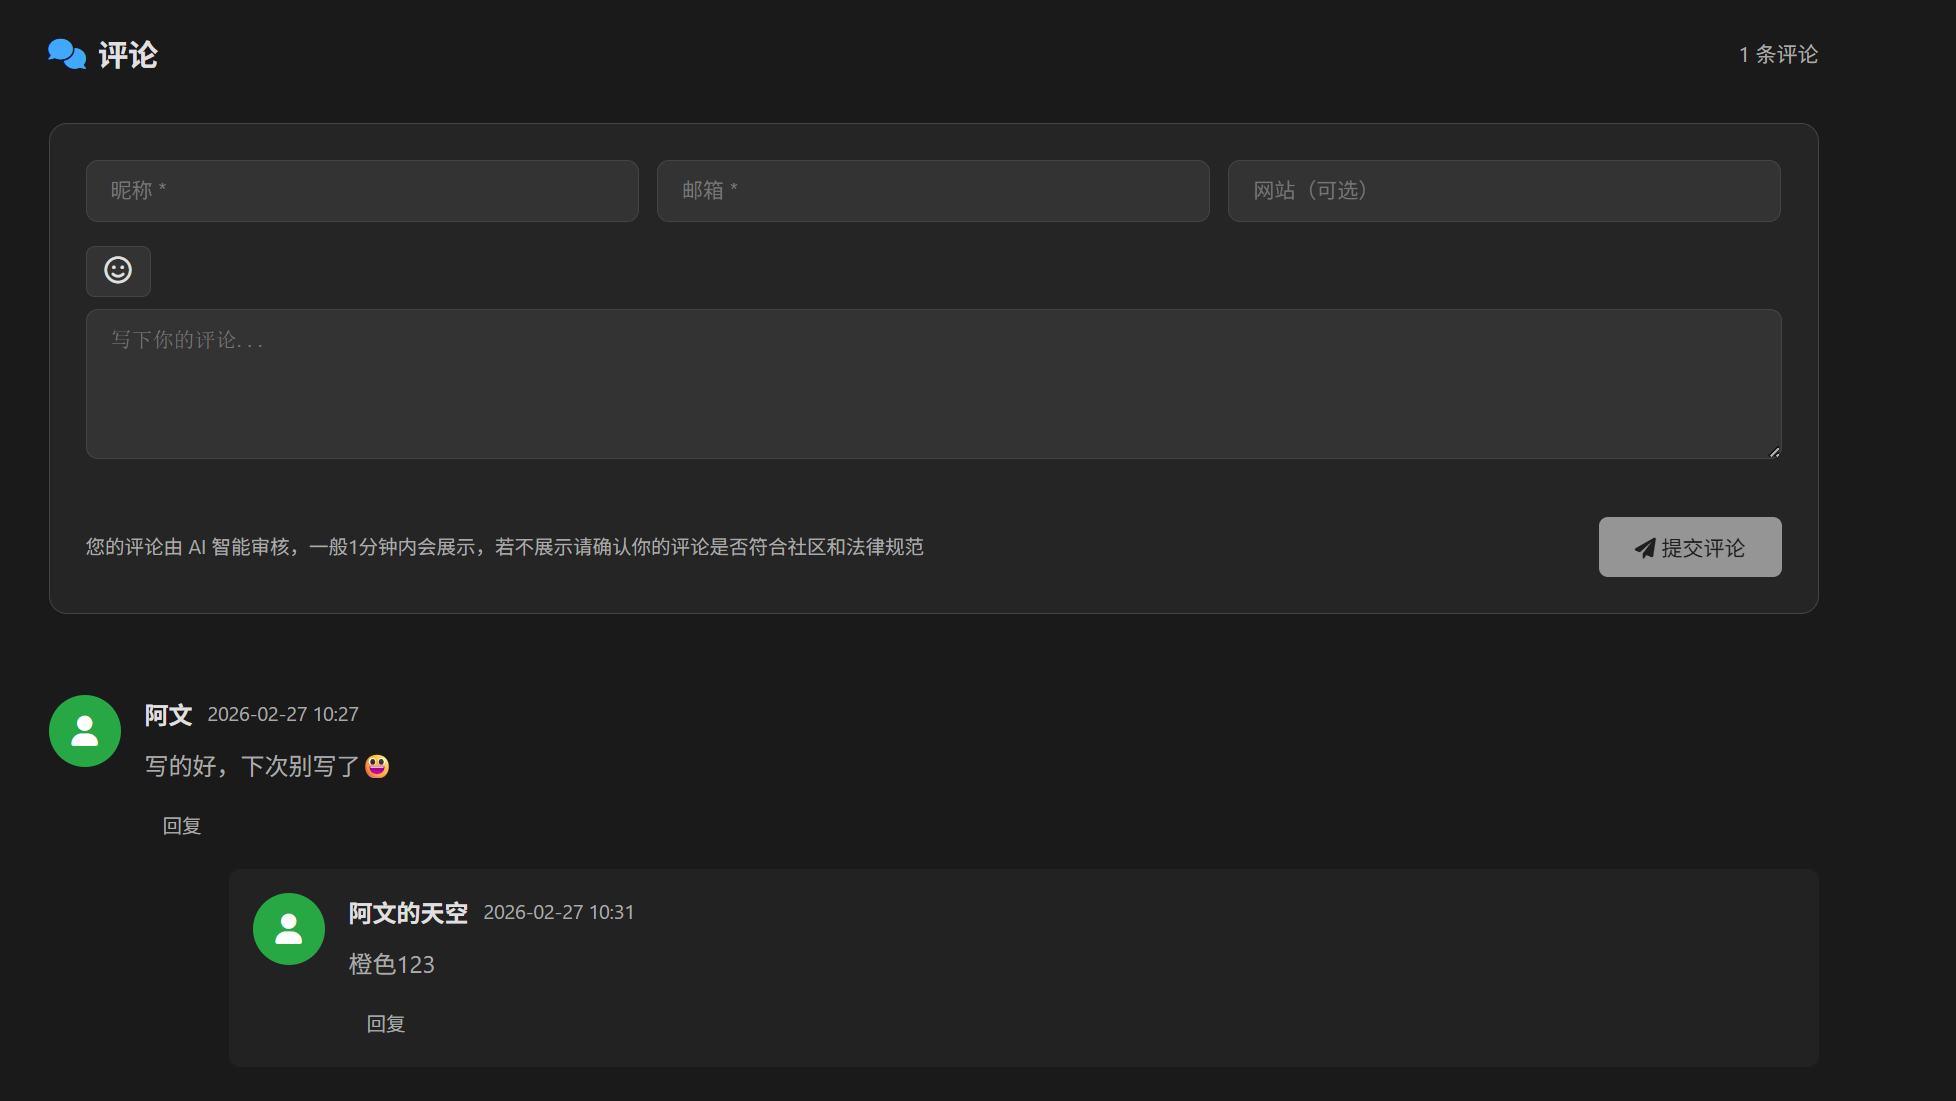
Comment features : post comments, reply to comments, paginated displayMulti-layer security : Referer validation, human verification, IP rate limiting, email rate limiting, content deduplicationContent moderation : AI automatic moderation + manual moderation as a dual safeguardAdmin backend : admin login, comment moderation, deletion, repliesData security : JWT authentication, soft delete, email masking
1.2 Overall Architecture ┌─────────────────────────────────────────────────────────────────┐limit (1 r/m) │ logging │8083 ) │8 │
1.3 Core Features
Feature
Technical implementation
Description
Origin validation
Referer middleware
Only allow comments from designated domains
Human verification
Cloudflare Turnstile
Invisible CAPTCHA replacing traditional CAPTCHA
Multi-layer rate limiting
Token Bucket
Triple rate limiting by IP + email + content fingerprint
Content moderation
Alibaba Cloud Bailian
AI-powered detection of violating content
Authentication/authorization
JWT
Stateless authentication, 7-day validity
Data masking
Runtime processing
Mask sensitive info like email and IP when displaying
2. Tech Stack Selection and Project Structure 2.1 Core Tech Stack go 1.21 .9 .1 .2 .0 .6 .0 .5 .0 .5 .4 .25 .7
2.2 Project Structure blog_api/ / / / / / / / / / / / /
3. The Multi-Layer Security System 3.1 Referer Origin Check Prevents malicious websites from submitting comments cross-site; only the designated domain is allowed:
package middlewareimport ("net/http" "strings" "github.com/gin-gonic/gin" func RefererCheck (allowedReferer string ) return func (c *gin.Context) "Referer" )"Origin" )if referer != "" && !strings.Contains(referer, allowedReferer) {"error" : "Illegal origin" })return if origin != "" && !strings.Contains(origin, allowedReferer) {"error" : "Illegal origin" })return
3.2 Cloudflare Turnstile Human Verification Replaces traditional CAPTCHA, offering a better user experience:
package servicesimport ("encoding/json" "fmt" "net/http" "net/url" "time" const turnstileVerifyURL = "https://challenges.cloudflare.com/turnstile/v0/siteverify" type TurnstileService struct {string type TurnstileVerifyResponse struct {bool `json:"success"` string `json:"challenge_ts"` string `json:"hostname"` string `json:"error-codes"` func NewTurnstileService (secretKey string ) return &TurnstileService{10 * time.Second},func (s *TurnstileService) string , remoteIP string ) (*TurnstileVerifyResponse, error ) {"secret" , s.secretKey)"response" , token)if remoteIP != "" {"remoteip" , remoteIP)if err != nil {return nil , fmt.Errorf("failed to verify turnstile: %w" , err)defer resp.Body.Close()var result TurnstileVerifyResponseif err := json.NewDecoder(resp.Body).Decode(&result); err != nil {return nil , errreturn &result, nil
3.3 JWT Authentication Middleware Admin operations require JWT authentication:
package middlewareimport ("net/http" "strings" "blog-api/pkg/jwt" "github.com/gin-gonic/gin" func Auth () return func (c *gin.Context) "Authorization" )if authHeader == "" {"error" : "Missing authentication information" })return " " , 2 )if len (parts) != 2 || strings.ToLower(parts[0 ]) != "bearer" {"error" : "Invalid authentication format" })return 1 ])if err != nil {"error" : "Invalid or expired token" })return "userID" , claims.UserID)"username" , claims.Username)
4. Database Design and Model Relationships 4.1 Data Model Design package modelsimport ("time" "github.com/google/uuid" "gorm.io/gorm" type Comment struct {string `json:"id" gorm:"type:char(36);primary_key"` string `json:"post_id" gorm:"type:varchar(200);not null;index;comment:'post ID/path'"` string `json:"parent_id,omitempty" gorm:"type:char(36);index;comment:'parent comment ID, for replies'"` string `json:"nickname" gorm:"type:varchar(50);not null"` string `json:"email" gorm:"type:varchar(100);not null"` string `json:"website" gorm:"type:varchar(200)"` string `json:"content" gorm:"type:text;not null"` string `json:"ip" gorm:"type:varchar(50);not null"` string `json:"user_agent" gorm:"type:varchar(500)"` int `json:"status" gorm:"type:tinyint;default:0;comment:'0-pending 1-approved 2-rejected'"` bool `json:"is_admin" gorm:"default:false"` `json:"created_at"` `json:"updated_at"` `json:"-" gorm:"index"` `json:"replies,omitempty" gorm:"foreignKey:ParentID"` func (c *Comment) error {if c.ID == "" {return nil func (Comment) string {return "comments"
4.2 Data Masking func (c *Comment) return CommentResponse{func maskEmail (email string ) string {if len (email) <= 3 {return emailmake ([]rune , 0 , len (email))for i, ch := range email {if i < 2 || ch == '@' {append (parts, ch)else {append (parts, '*' )return string (parts)
package handlersfunc (h *CommentHandler) var req models.CreateCommentRequestif err := c.ShouldBindJSON(&req); err != nil {"error" : "Invalid request parameters: " + err.Error()})return if h.turnstileService != nil {if err != nil || !result.Success {"error" : h.turnstileService.GetErrorMessage(result.ErrorCodes),return "User-Agent" )0 , false ,if err := h.db.Create(comment).Error; err != nil {"error" : "Failed to create comment" })return if h.auditService != nil {": " + req.Contentgo h.asyncAuditComment(comment.ID, auditText)"message" : "Comment submitted successfully; it will display automatically once approved" ,"data" : comment.ToResponse(),
func (h *CommentHandler) "post_id" )if postID == "" {"error" : "Missing post ID parameter" })return "page" , "1" ))"page_size" , "20" ))var comments []models.Comment"post_id = ? AND status = ? AND parent_id IS NULL" , postID, 1 )."created_at DESC" ).1 ) * pageSize)."Replies" , func (db *gorm.DB) return db.Where("status = ?" , 1 ).Order("created_at ASC" )if err != nil {"error" : "Failed to fetch comments" })return var responses []models.CommentResponsefor _, comment := range comments {append (responses, comment.ToResponse())"data" : responses,"pagination" : gin.H{"page" : page,"page_size" : pageSize,
6. Smart Content Moderation System 6.1 Alibaba Cloud Bailian AI Moderation Using the Alibaba Cloud Bailian app for smart content moderation:
package servicesimport ("bytes" "encoding/json" "fmt" "io" "net/http" "time" type AliyunAuditService struct {string string func NewAliyunAuditService (apiKey, appID string ) return &AliyunAuditService{30 * time.Second},func (s *AliyunAuditService) string ) (bool , error ) {"https://dashscope.aliyuncs.com/api/v1/apps/%s/completion" , s.appID)map [string ]interface {}{"input" : map [string ]interface {}{"prompt" : content,"biz_params" : map [string ]interface {}{"user_defined_params" : map [string ]interface {}{"content" : content,"parameters" : map [string ]interface {}{},"debug" : map [string ]interface {}{},"POST" , url, bytes.NewBuffer(jsonData))"Authorization" , "Bearer " +s.apiKey)"Content-Type" , "application/json" )if err != nil {return false , errdefer resp.Body.Close()var apiResp struct {struct {string `json:"text"` `json:"output"` if err := json.Unmarshal(body, &apiResp); err != nil {return false , errvar auditResult struct {bool `json:"status"` if err := json.Unmarshal([]byte (apiResp.Output.Text), &auditResult); err != nil {return false , errreturn auditResult.Status, nil
6.2 Asynchronous Moderation Flow func (h *CommentHandler) string , auditText string ) {if err != nil {"Audit failed for comment %s: %v" , commentID, err)return var status int if passed {1 "Comment %s audit passed" , commentID)else {2 "Comment %s audit rejected" , commentID)if err := h.db.Model(&models.Comment{}).Where("id = ?" , commentID).Update("status" , status).Error; err != nil {"Failed to update comment %s status: %v" , commentID, err)
7. Rate Limiting and Anti-Spam Mechanism package ratelimitimport ("crypto/sha256" "encoding/hex" "fmt" "net/http" "strings" "sync" "time" "github.com/gin-gonic/gin" "golang.org/x/time/rate" type CommentRateLimiter struct {map [string ]*Visitorint map [string ]*Visitorint map [string ]time.Time func NewCommentRateLimiter (ipPerMinute, emailPerMinute int ) make (map [string ]*Visitor),1 , make (map [string ]*Visitor),1 ,make (map [string ]time.Time),10 ,go c.cleanup()return cfunc (c *CommentRateLimiter) return func (ctx *gin.Context) if ctx.Request.Method != http.MethodPost {return if !ipLimiter.Allow() {"error" : "Submitting too frequently, please try again later (IP limit)" ,return if email != "" {if !emailLimiter.Allow() {"error" : "This email is submitting too frequently, please try again later" ,return
7.2 Content Duplicate Detection func (c *CommentRateLimiter) string ) bool {defer c.contentMu.Unlock()if lastTime, exists := c.contentCache[fingerprint]; exists {if time.Since(lastTime) < c.contentTTL {return true return false func (c *CommentRateLimiter) string ) string {if len (cleaned) > 100 {100 ]byte (cleaned))return hex.EncodeToString(hash[:]) + fmt.Sprintf("_%d" , len (content))
8. Deployment and Operations Practice 8.1 Nginx Multi-Layer Rate-Limit Configuration limit_req_zone $binary_remote_addr zone=comment:10m rate=1r/m;server {listen 443 ssl http2;server_name blogapi.awen.me;location /api/v1/comments {limit_req zone=comment burst=5 nodelay;limit_req_status 429 ;proxy_pass http://127.0.0.1:8083;proxy_set_header Host $host ;proxy_set_header X-Real-IP $remote_addr ;proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for ;location / {proxy_pass http://127.0.0.1:8083;proxy_set_header Host $host ;proxy_set_header X-Real-IP $remote_addr ;
8.2 systemd Service Configuration [Unit] Description =Blog API ServerAfter =network.target mysqld.serviceRequires =mysqld.service[Service] Type =simpleUser =rootWorkingDirectory =/opt/blog-apiExecStart =/usr/bin/blog-apiEnvironment ="SERVER_PORT=8083" Environment ="SERVER_MODE=production" Environment ="ALLOWED_REFERER=www.awen.me" Environment ="DB_HOST=localhost" Environment ="DB_PORT=3306" Environment ="DB_USER=blog_api_user" Environment ="DB_PASSWORD=your_password" Environment ="DB_NAME=blog_api_db" Environment ="JWT_SECRET=your_jwt_secret_key" Environment ="JWT_EXPIRES_IN=168h" Environment ="COMMENT_RATE_LIMIT_IP=2" Environment ="COMMENT_RATE_LIMIT_EMAIL=2" Environment ="ALIYUN_API_KEY=your_api_key" Environment ="ALIYUN_APP_ID=your_app_id" Environment ="TURNSTILE_SECRET_KEY=your_secret_key" Restart =alwaysRestartSec =10 [Install] WantedBy =multi-user.target
8.3 Deployment Script #!/bin/bash set -e"blog-api" "your-server" "/opt/blog-api" echo "=== Building... ===" ${APP_NAME} cmd/main.goecho "=== Deploying to ${SERVER_HOST} ... ===" ${APP_NAME} root@${SERVER_HOST} :${SERVER_DIR} /echo "=== Restarting service... ===" ${SERVER_HOST} "systemctl restart blog-api" echo "=== Checking status... ===" ${SERVER_HOST} "systemctl status blog-api --no-pager" echo "=== Deploy complete! ==="
9. Summary and Outlook 9.1 Project Highlights
Multi-layer security system
Referer origin check preventing cross-site submission
Cloudflare Turnstile invisible human verification
Triple rate limiting by IP + email + content fingerprint
JWT stateless authentication
Smart content moderation
Alibaba Cloud Bailian AI automatic moderation
Asynchronous processing that doesn’t block users
Manual moderation as a fallback
Complete comment features
Nested reply support
Paginated display
Data masking protecting privacy
Multi-layer rate-limit protection
Nginx-layer rate limiting (1r/m)
Application-layer IP rate limiting
Application-layer email rate limiting
Content fingerprint deduplication
Metric
Value
Description
API response time
< 50ms
Local test
AI moderation time
500ms - 2s
Asynchronous processing
Database query
< 10ms
Indexed
Concurrency
1000+ QPS
Load-test data
9.3 Future Optimization Directions
Email notifications : email the user when a comment is replied toSensitive-word filtering : a local sensitive-word dictionary + AI moderation as a dual safeguardAnti-spam enhancement : add device fingerprinting and behavior analysisAdmin backend : a web-visualized backend for managing commentsData export : support exporting and backing up comment data
References
评论
0 条评论